What is included
- Vulnerability assessmentAutomated and manual testing of your applications, APIs and infrastructure.
- Penetration testingScoped attacks against your systems, documented with reproduction steps and business impact.
- Secure code reviewA read through the code paths that handle authentication, payments and personal data.
- Access & permission auditsWho can reach what across Microsoft 365, SharePoint and your cloud accounts — usually a surprise.
- HardeningConfiguration, patching, backup verification and monitoring set up so problems are noticed.
- Compliance preparationEvidence, policies and gap analysis for ISO 27001, GDPR and SOC 2 readiness.
Tools we use
OWASP ASVSBurp SuiteNessusMicrosoft DefenderAzure SentinelISO 27001
What you receive
- Working softwareDeployed to your accounts, in your repository.
- DocumentationWritten for the person who maintains it next, not for us.
- A walkthroughA recorded handover session with your team.
- Support windowIncluded after launch, extendable monthly.
Results from this work
Figures from projects we have delivered in this area.
100%of critical findings retested
2 wkmedian time to remediation
0findings left unexplained
Questions we get asked
Will testing take our systems down?
No. Testing is scoped and scheduled with you, destructive tests are excluded by default, and we can work against a staging copy.
What do we get at the end?
An executive summary, a technical report with severity and reproduction steps, a fix plan, and a free retest once you have made the changes.
Related services
These usually travel together.
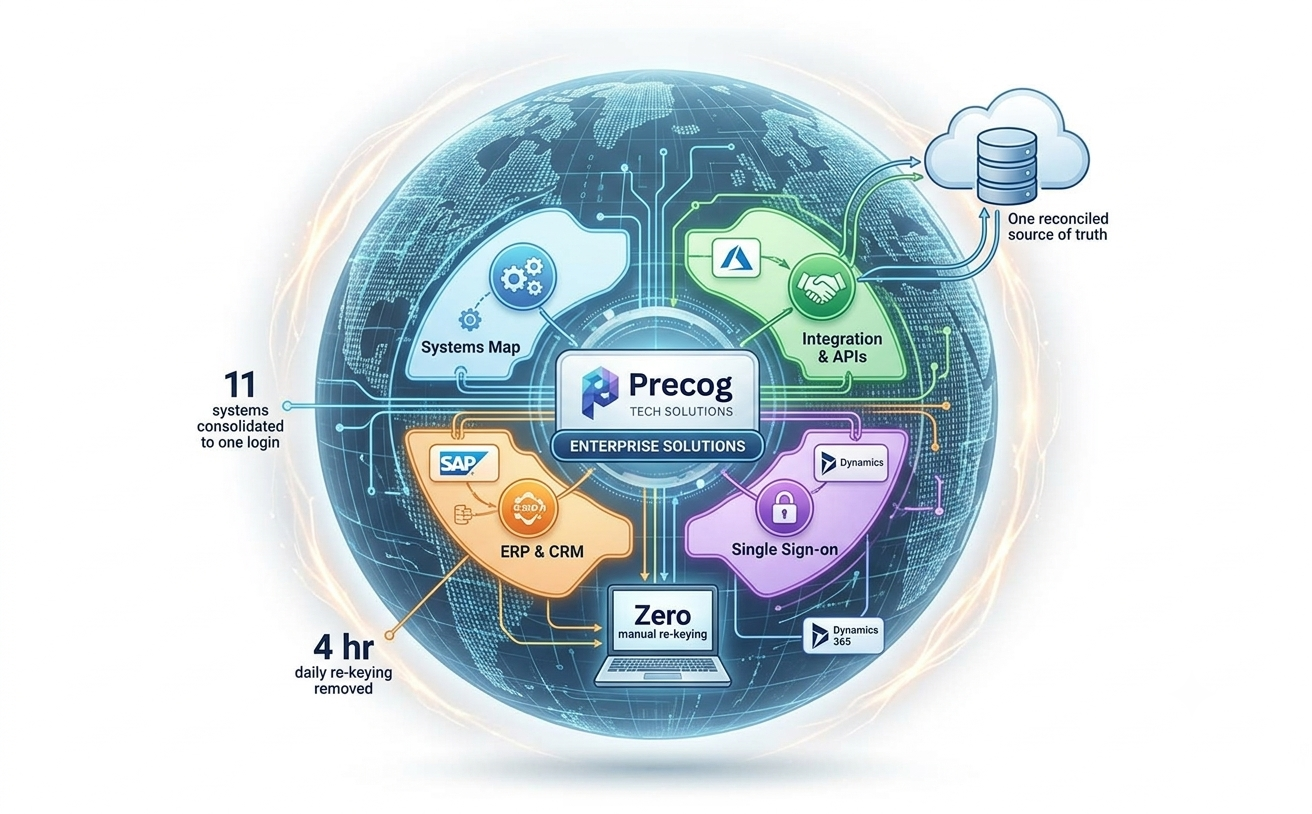
Enterprise solutions
ERP and CRM integration, single sign-on, and the connective tissue between systems that never spoke.
- Azure Integration Services
- Power Automate
- REST & GraphQL
- Dynamics 365
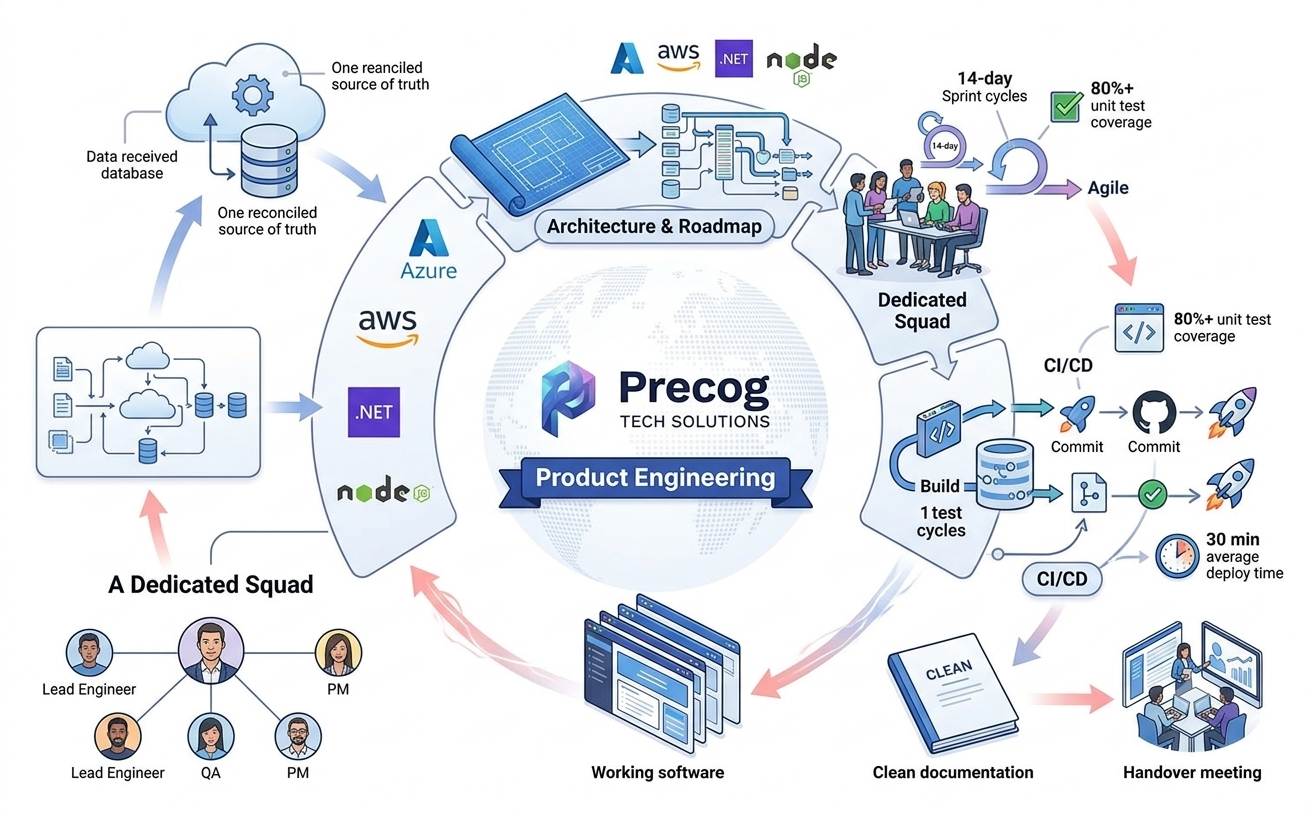
Product engineering
Architecture, roadmap, CI/CD and a dedicated squad for teams building a product, not a project.
- Azure
- AWS
- .NET
- Node.js
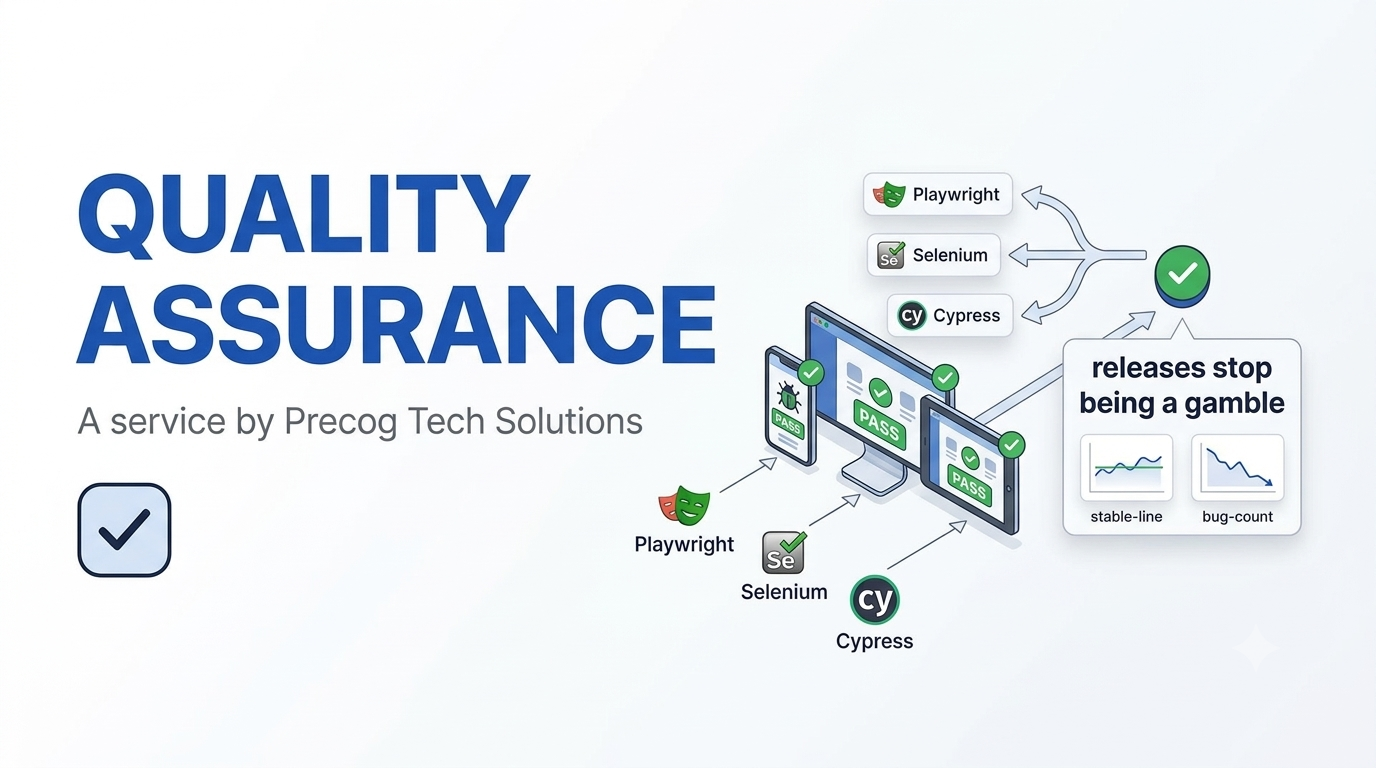
Quality assurance
Manual and automated testing across devices and edge cases, so releases stop being a gamble.
- Playwright
- Selenium
- Cypress
- Postman
Ready to talk about cyber security?
Tell us the problem in a few lines. You will get a written estimate within 48 hours of a discovery call.